
Security
How Kyro protects your keys
Kyro keeps your keys encrypted on your computer and asks you to confirm every signature in a system window. Here is what that covers, and what it does not.
Design
Three layers, one place for keys
The interface you click is a sandboxed web view. It never sees a key. Keys live only in the Rust core, which encrypts them, signs and returns the signed transaction.
- Recovery phrase and keys encrypted with your password: Argon2id, then XChaCha20-Poly1305.
- Stored only on your computer. No copy on a server, no cloud backup.
- Standard 12 or 24-word BIP39 recovery phrases.
Before you sign
Nothing is signed without you
Every signature needs your password and a confirmation in a native system window, drawn by the app shell rather than the web view.
- The window shows the decoded transaction: amount, recipient, fee, account.
- Unusual transactions ask for a second confirmation: contract calls, any token approval, value sent to a contract, an unknown chain ID, high fees.
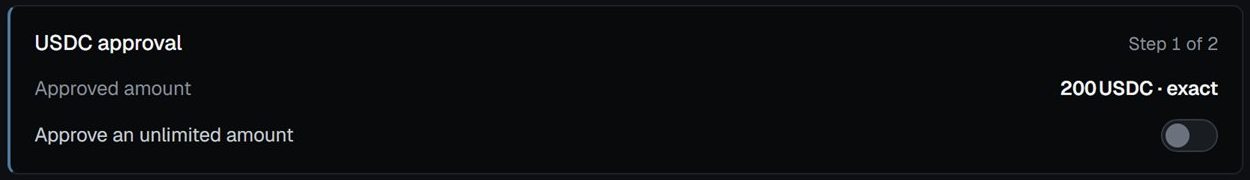
- Token approvals are for the exact amount by default.
- Address-poisoning alerts and clipboard checks before you send.
Network
Private by default
Kyro talks to blockchains over Tor, which is built into the app. Your IP address is not linked to your addresses.
- A separate Tor circuit per blockchain.
- If Tor fails, Kyro stops. It never falls back to a direct connection.
- Every server Kyro contacts is listed in NETWORK.md.
- Use your own node or server for each blockchain.
- No telemetry, no analytics, no account.
Limits
What Kyro cannot protect you from
No wallet can. Knowing these helps you avoid them.
- Malware with full control of your computer while the wallet is unlocked.
- Anyone who gets your recovery phrase. Kyro never asks for it outside the app, and neither should anyone else.
- A transaction you read and confirm. Check the recipient and amount in the system window every time.
- A lost recovery phrase. Kyro has no copy and cannot reset it. Write it on paper and keep it offline.
Audit status
Kyro is open source under GPL-3.0-or-later, so anyone can review it. An internal security review has been done. No external audit has been published yet. Kyro is provided without warranty, as stated in the license.
Report a vulnerability
Please report security issues privately through GitHub security advisories, not in a public issue. The security policy explains what is in scope and how reports are handled.
Get Kyro
Version 1.0.0 · Free · Windows, macOS and Linux